Zero trust architecture, conditional access, security baselines, and identity.
9 articles
A default member in Entra ID can enumerate the whole directory: every user, group, service principal and role assignment. The controls that narrow it.
What an M365 Solution Architect actually does: standards ownership, security architecture, licensing strategy, and delivery oversight. Beyond diagrams.
Compare Intune security baselines against CIS benchmarks with a PowerShell export-and-diff workflow: ASR deployment and deviation tracking included.
M365 E3 vs E5 decision framework for architects: TCO breakpoints, cost comparison scripts, and the rule for when E5 actually beats E3 plus add-ons.
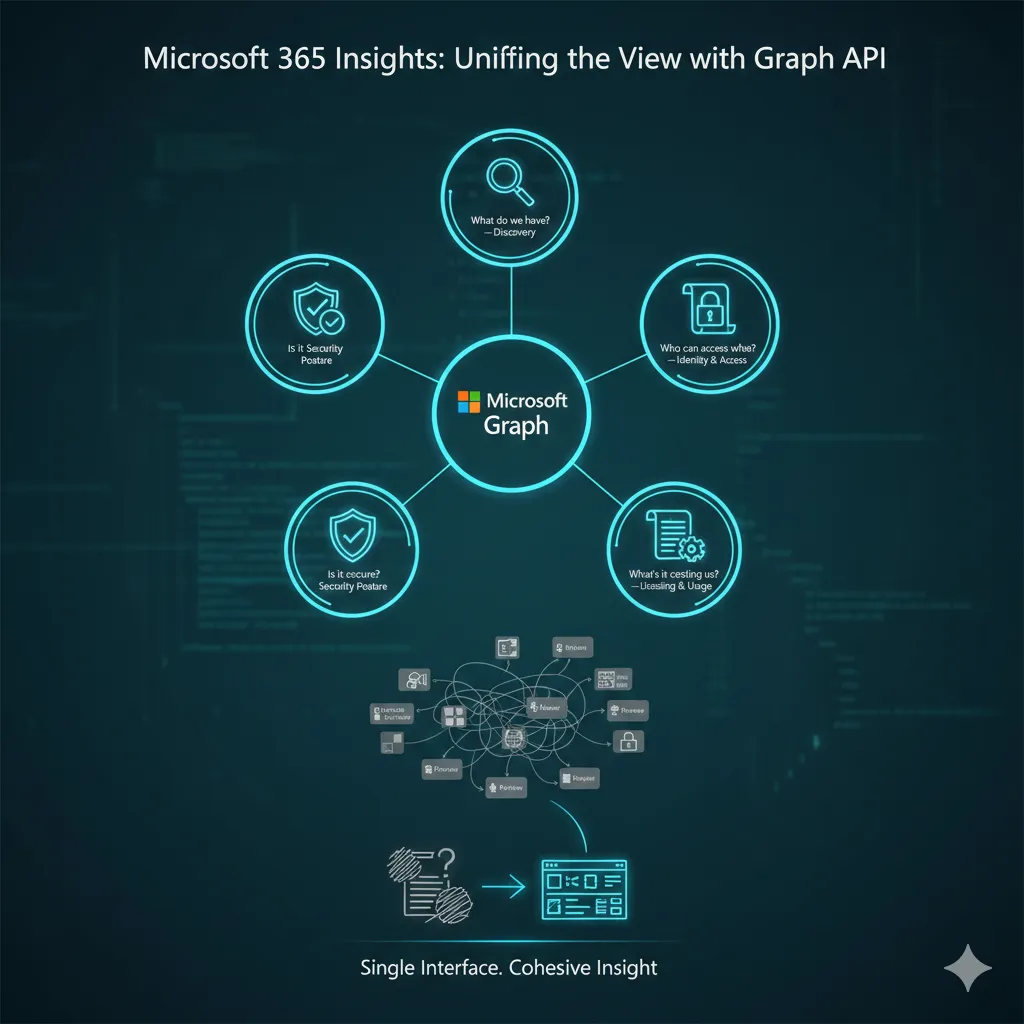
Microsoft 365 tenant health audit checklist: detect orphaned groups, expired app secrets, CA policy sprawl, and SharePoint chaos with Graph API scripts.
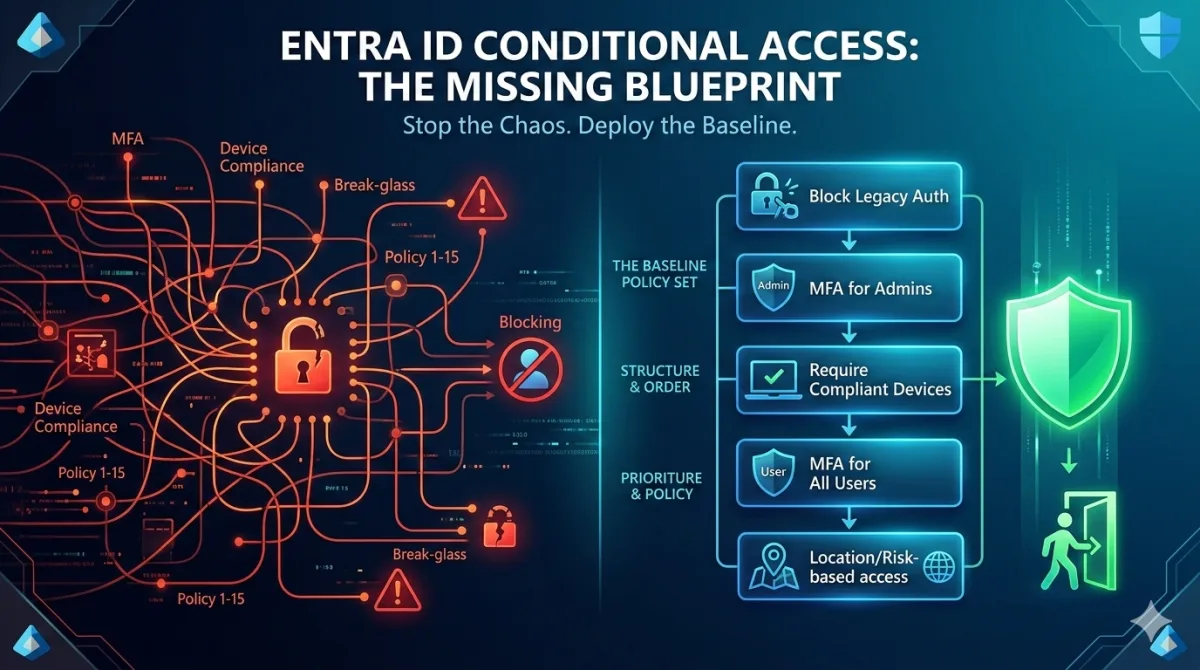
A baseline Conditional Access policy set built from 20 deployments: common mistakes, circular dependencies, and the patterns that survive production.
Production-ready PowerShell scripts for M365 tenant assessment via Graph API: discovery, identity auditing, security posture, governance, licensing.
How to build a repeatable, auditable Windows estate using Intune, Autopilot, and GitOps: the foundation for Zero Trust and Copilot-ready endpoints.
A practical look at Microsoft's Global Secure Access SSE solution: what it does, how it works, and where it fits in a zero-trust architecture.