sbd.org.ukNo. 01
This issue
Access and networks
- + Global Secure Access: Microsoft's SSE Play
- + Azure Virtual Desktop Architecture Principles
- + Homelab VLANs and DNS-Based Policy Routing
This issue
Microsoft 365
A practical look at Microsoft's Global Secure Access SSE solution: what it does, how it works, and where it fits in a zero-trust architecture.
By Paul Bentley · 10 min read
Global Secure Access (GSA) is the umbrella name for Microsoft Entra Internet Access and Microsoft Entra Private Access, built into the Entra platform. Microsoft pairs these two with Microsoft Defender for Cloud Apps, its cloud access security broker (CASB), to complete its Security Service Edge (SSE) solution. Together, the three converge into one identity-aware control plane covering zero-trust network access (ZTNA), secure web gateway (SWG) and CASB controls.
The pitch is straightforward. Rather than bolting on third-party SSE products that have no awareness of your identity platform, GSA pulls network security into the same control plane as Entra ID, Conditional Access and endpoint management. That trade-off, tighter integration versus best-of-breed flexibility, is the question this post answers.
Infrastructure
Architecture principles for Azure Virtual Desktop: host pool design, FSLogix, MSIX App Attach, image lifecycle, and monitoring, from real deployments.
By Paul Bentley · 10 min read
Azure Virtual Desktop has matured since its initial release. What was once a complex, sprawling service requiring deep Azure networking expertise is now a viable enterprise VDI platform. But maturity in the product doesn't guarantee maturity in implementations. I've seen AVD deployments that replicate every anti-pattern from legacy Citrix environments, and others that embrace cloud-native principles and end up with a platform that costs less to run.
This post distils the architectural principles I apply when designing AVD solutions. It's not a step-by-step deployment guide; Microsoft's documentation covers that adequately. Instead, it focuses on the decisions that determine whether your AVD platform becomes an asset or a liability.
Infrastructure
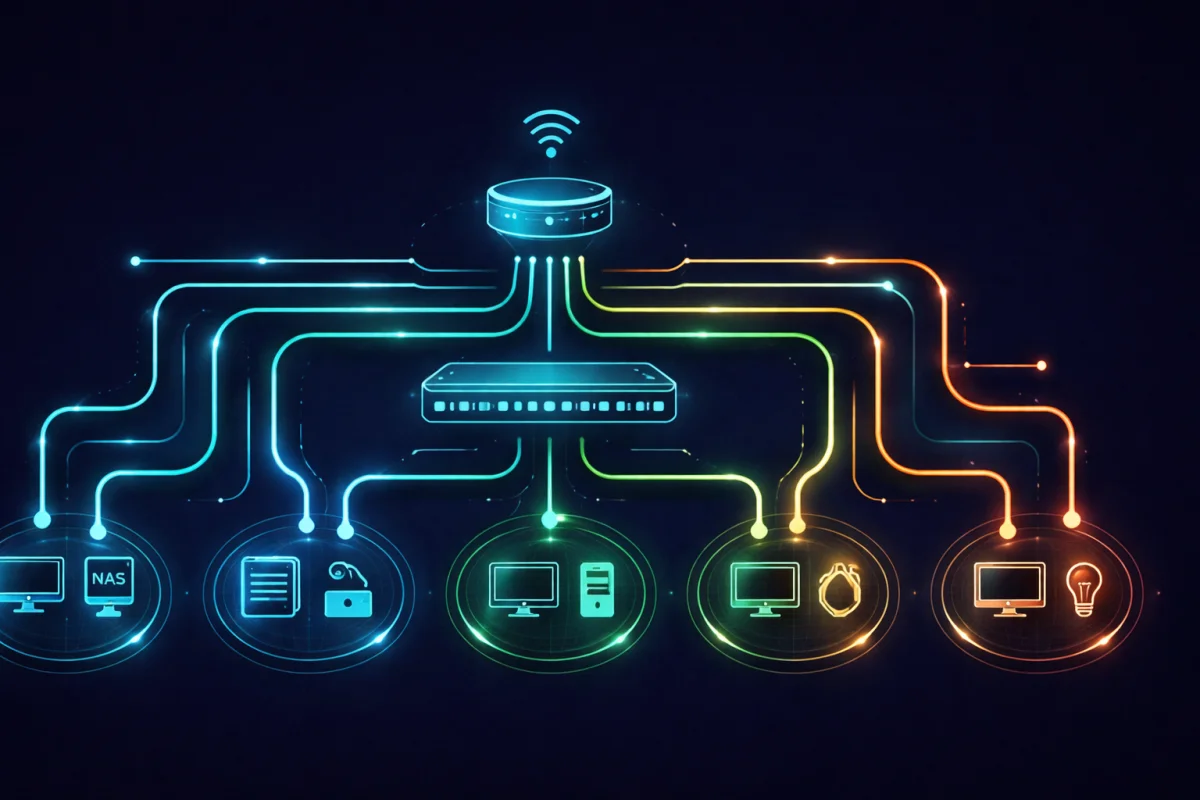
How I segment a homelab with VLANs and route traffic through country-specific VPN tunnels, driven by a YAML intent file and Jinja2 templates on OpenWRT.
By Paul Bentley · 9 min read
Most homelabs start as a flat network. A NAS, a few Docker containers, some IoT devices, maybe a Proxmox host, all share the same subnet, the same default gateway, the same path to the internet. It works fine until you start asking questions like "why can my smart plug talk to my backup server?" or "can I route BBC iPlayer through a UK exit without affecting everything else on this VLAN?"
This post describes the network as I first built it. By September 2026 it had grown: the router is now a high availability pair, there are more VLANs, the VPN tunnels form a failover pool, and deployment runs per node with health checks and automatic rollback. The routing approach below is unchanged.
These are the questions that turned my flat network into a VLAN-segmented, policy-routed setup running on an OpenWRT instance inside a Proxmox LXC. The result is a system where adding a new domain to a specific VPN tunnel is a one-line YAML change, and the entire network configuration is rendered from templates, with no manual edits on the router, ever.
Long, specific write-ups on M365 architecture and security, worked out against real tenants rather than summarised from documentation. Sent rarely, and only when it is worth your time.